
For fewer than 150 mailboxes, run a cutover migration. Above that, or for tenant-to-tenant scenarios like mergers and divestitures, use a phased approach built on Migration Orchestrator. Either way, your first move today is the same: run a discovery inventory and validate identity and licensing before you touch a single mailbox.
TL;DR:
- Migration timing depends on organization size; small setups can use a quick cutover, while larger or tenant-to-tenant moves require phased or orchestrator-based approaches lasting several months.
- Critical prerequisites include mapping identities before licensing, reducing DNS TTL early, and aligning Azure AD Connect schedules with the migration window to prevent delays.
- Native tools like Migration Orchestrator handle core workloads but may require third-party solutions for complex SharePoint, regulatory, or device migration needs.
- Migration sequencing matters; mailboxes must move before Teams meetings, and dependency-aware batching minimizes legal holds and scheduling limits.
- Validating the migration involves testing mail flow, connectivity, and data integrity, with a comprehensive rollback plan supporting 30 to 60 days post-migration.
Table of Contents
- What Are the Microsoft 365 Migration Models and When Do You Use Each?
- Which Workloads Move First in an Office 365 Migration?
- What Prerequisites Do You Need Before You Migrate?
- Which Tools Should You Use: Native Microsoft or a Third Party?
- How Long Does a Microsoft 365 Migration Actually Take?
- What Security Controls Should Be in Place Before Data Lands?
- How Do You Validate the Migration and Plan for Rollback?
- Total Cyber Solutions’ Perspective on Managed Migrations
- Ready to Plan Your Microsoft 365 Migration?
- Sources
- FAQ
What Are the Microsoft 365 Migration Models and When Do You Use Each?
Four architectures cover almost every real-world scenario. Picking the wrong one is how a weekend project turns into a six-month fire drill.
- Cutover: everything moves in one event, typically under 150 mailboxes. Fast, but a single point of failure.
- Staged: mailboxes move in scheduled batches over weeks, common for 150 to a few thousand users.
- Hybrid: on-premises Exchange coexists with Exchange Online during a longer transition, often for larger, IT-mature organizations.
- Tenant-to-tenant: moving between two Microsoft 365 tenants entirely, driven by mergers, acquisitions, or divestitures.
Tenant-to-tenant work should be planned identity-first, with the architecture chosen as single-event, phased, or a tenant move/split depending on how much the business can absorb at once. A single cutover event across 3,000 mailboxes concentrates every risk into one weekend. Phasing spreads that risk but demands tighter identity mapping discipline.
Which Workloads Move First in an Office 365 Migration?
Sequencing matters more than most admins expect. Exchange mailboxes have to land before Teams meetings, because meeting data references mailbox calendar items that don’t exist yet if the mailbox hasn’t moved.
OneDrive and SharePoint carry their own dependencies. Chat files in Teams live in OneDrive, and Teams group metadata maps back to SharePoint sites, so migrating “Teams” really means migrating three interconnected workloads at once.
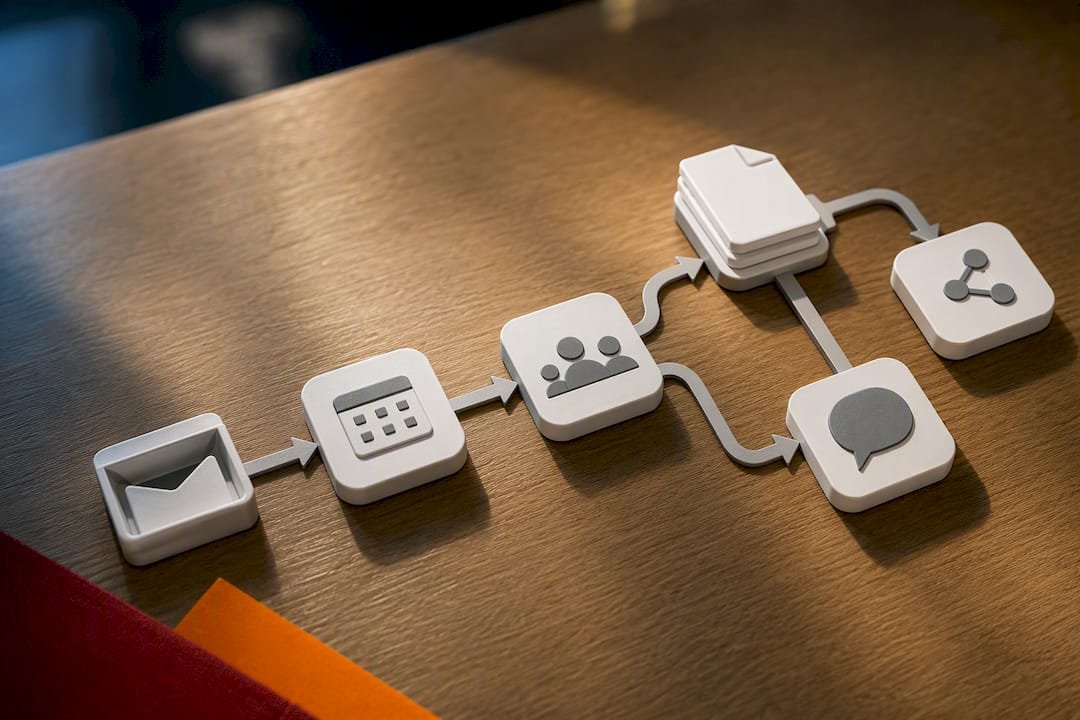
Migration Orchestrator coordinates four supported workloads: Exchange mailboxes, OneDrive, Teams chats, and Teams meetings. It moves content, not identities, and it does not touch shared Teams channels or SharePoint sites. Those need separate handling through Migration Manager or SPMT.
Two operational limits catch teams off guard every time:
- Mailboxes or OneDrive accounts on litigation, retention, or eDiscovery hold are blocked from migration outright until legal clears the hold.
- OneDrive migrations run against daily scheduling limits, so large batches queue rather than run instantly.
Running multi-workload batches together, rather than isolating each workload, lets the Orchestrator manage these dependencies instead of you managing them manually.
What Prerequisites Do You Need Before You Migrate?
Get these wrong and you’ll spend more time on remediation than on the actual migration.
- Map identities first. Cross-tenant identity mapping (CTIM) has to write ExchangeGuid, ArchiveGuid, and LegacyExchangeDN attributes on the target mailbox before that mailbox gets licensed.
- Sequence licensing carefully. Confirm target licenses, including cross-tenant add-ons, are provisioned and ready before any move starts, but never assign the mailbox license until identity mapping is complete.
- Lower DNS TTL early. Drop your TTL well ahead of the MX record change so cutover propagates fast instead of leaving mail stuck in limbo for 24 to 48 hours.
- Plan network throughput. Mailbox size drives migration duration directly, so estimate bandwidth needs against your largest mailboxes, not your average ones.
- Time Entra Connect (Azure AD Connect) correctly. Sync schedules need to align with your cutover window, not run independently of it.
Pro Tip: If you license a target mailbox before CTIM finishes writing the Exchange GUID attributes, Exchange Online provisions a brand-new empty mailbox instead of recognizing the migrated one. Unpicking that mistake by hand can add days to your timeline.
Which Tools Should You Use: Native Microsoft or a Third Party?
Migration Orchestrator handles the four core workloads (Exchange mailboxes, OneDrive, Teams chats, Teams meetings) and manages the sequencing between them automatically. It’s the right starting point for most tenant-to-tenant projects.
For files and SharePoint specifically, Migration Manager and SPMT are the current native tools. Mover, the older third-party tool Microsoft once recommended, has been retired into these Migration Manager paths.
FastTrack can add hands-on assistance for eligible Exchange and file migrations, and it publishes its own prerequisites so you know exactly what’s in and out of scope before you request help.
Reach for a partner or third-party tool when your situation goes beyond what native tools cover:
- Complex Teams channel restructuring or renaming during the move
- Regulatory reporting requirements that need custom audit trails
- Incremental or delta sync needs beyond a single cutover event
- Device migration for Intune-managed or hybrid-joined endpoints, which is often the most labor-heavy part of the whole project
How Long Does a Microsoft 365 Migration Actually Take?
Most of the calendar time goes to planning, not data movement. The actual data transfer typically accounts for only 20 to 30 percent of total project time. The rest is discovery, security configuration, testing, and getting users ready.
The runbook breaks into seven phases:
- Discovery: inventory mailboxes, OneDrive accounts, Teams, and shared data; flag anything on hold.
- Architecture: pick cutover, staged, hybrid, or tenant-to-tenant based on size and business driver.
- Pilot: validate mail flow, Autodiscover, and delta sync policies with a small user group.
- Waves: move batches on schedule, with network, identity, and helpdesk teams each owning their piece.
- Cutover: flip MX records and DNS after TTL has dropped and mail flow tests pass clean.
- Stabilization: watch for delivery delays, sync errors, and helpdesk ticket spikes for the first week.
- Optimization: clean up stale licenses, retire legacy connectors, tune retention policies.
Mailbox move duration scales with size. Microsoft’s own telemetry shows mailboxes under 10 GB typically finish in about a day, while large consolidations involving thousands of bigger mailboxes stretch into multi-month projects with throttling limiting how many moves run in parallel.
| Organization size | Typical model | Rough timeline |
|---|---|---|
| Under 150 mailboxes | Cutover | Short-duration event |
| 150 to a few thousand mailboxes | Staged / phased | Weeks-long process |
| Above that, or for tenant-to-tenant | Orchestrator-led phased or hybrid | Extended multi-month process |
What Security Controls Should Be in Place Before Data Lands?
Turning on security after migration is backwards. The safer sequence enables controls before the first batch moves.
- Enable Defender for Office 365, DLP policies, and sensitivity labels ahead of any content migration.
- Put retention and eDiscovery policies into audit mode first so you can see what they’d catch before enforcing them.
- Roll out Conditional Access in stages, and keep break-glass accounts with emergency exclusions ready in case a policy locks out a legitimate admin mid-migration.
- Loop in legal early. Any mailbox or OneDrive account under an active hold is blocked from migrating until that hold is resolved, and legal is usually the only team that can clear it.
Pro Tip: Run your Conditional Access rollout in report-only mode for at least a week before enforcing it. Migrations generate a lot of unusual sign-in activity, and a policy enforced too early can flag legitimate migration traffic as a threat. For a deeper walkthrough of hardening email specifically, see this Microsoft 365 email security guide.
How Do You Validate the Migration and Plan for Rollback?
Validation isn’t optional, and neither is a realistic rollback plan. Test these before declaring victory:
- Send test mail in four directions: internal to internal, internal to external, external to internal, and external to external.
- Check Autodiscover and Outlook profile connections on a sample of migrated users.
- Spot-check Teams chat history and OneDrive file integrity for a handful of accounts per batch.
- Keep coexistence and mail forwarding active as your practical rollback option once MX records have changed. A true rollback to the old system is rarely realistic after cutover.
- Hold the source environment for 30 to 60 days before decommissioning anything, and keep monitoring governance settings during that window.
Total Cyber Solutions’ Perspective on Managed Migrations
Veteran-owned and built around managed IT and cybersecurity, Total Cyber sees the same failure pattern across regulated industries: internal teams that know Microsoft 365 well but don’t have the bandwidth to run identity mapping, security staging, and a seven-phase runbook simultaneously.
A managed engagement makes the most sense for complex tenant-to-tenant moves, regulated organizations juggling compliance frameworks like HIPAA or CMMC, and any team stretched too thin to own every wave. A typical managed engagement starts with a discovery call, scopes the workloads and identity dependencies, then builds a phased plan before anything moves.
— Alden
Ready to Plan Your Microsoft 365 Migration?
A managed service is an alternative to running this migration blind. Instead of piecing together Orchestrator settings, identity mapping rules, and security staging on your own, you can work with a partner experienced in sequencing these moves for regulated and complex environments.
A migration assessment starts with a straightforward conversation about your tenant, your workloads, and your timeline. From there, Total Cyber typically offers:
- A discovery call to map mailboxes, OneDrive accounts, Teams data, and anything under legal hold
- A scope assessment that flags identity and licensing risks before they become remediation projects
- A phased plan sequenced by workload dependency, not guesswork
If your organization is weighing a cutover, a staged move, or a full tenant-to-tenant transition, schedule a Microsoft 365 migration assessment with Total Cyber and get a plan built around your actual environment rather than a generic template. For ongoing cloud operations after the move, Total Cyber’s managed services team can also handle what comes next.
Sources
- Plan a Microsoft 365 tenant-to-tenant migration | Microsoft Learn
- FastTrack migration learning center — prerequisites
FAQ
What Is a Microsoft 365 Migration?
It’s the process of moving mailboxes, files, and Teams data into Microsoft 365, either from on-premises systems or from another Microsoft 365 tenant, using a defined architecture like cutover, staged, or tenant-to-tenant.
What Is the Migration Tool for Microsoft 365?
Migration Orchestrator is Microsoft’s native tool for coordinating Exchange mailboxes, OneDrive, Teams chats, and Teams meetings during cross-tenant moves, while Migration Manager and SPMT handle file shares and SharePoint separately.
Can I Transfer My Microsoft 365 Account From One Computer to Another?
Yes. Microsoft 365 licenses and data live in the cloud, so signing into a new device with the same credentials restores access without any migration steps at all.
What Are the Different Types of Migration in Office 365?
The four main types are cutover (single event, small organizations), staged (batched over weeks), hybrid (coexistence with on-premises Exchange), and tenant-to-tenant (moving between two Microsoft 365 tenants entirely).
When Should I Hire a Managed Service Instead of Migrating In-House?
Consider a managed engagement for tenant-to-tenant moves, regulated industries with compliance obligations, or when internal IT lacks the bandwidth to run identity mapping and security staging alongside daily operations.